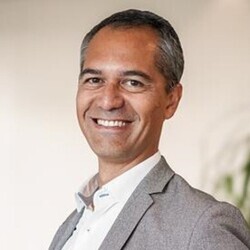
Vetea Lucas
Global VP IT Security, Risk and Compliance
Akkodis


My experience includes leading enterprise-wide crisis response and resilience programs, strengthening governance frameworks, and scaling global security operations in multi-country organizations. I operate at the intersection of cyber risk, executive governance, and operational resilience.
A fun fact about me, I love practicing many risky activities in my personal life, whether snowboarding in the wild, driving sport cars on tracks or freedive spearfishing. This is interesting in a role where it can be easy to become risk averse; I use it to balance my decisions.
Learn more about the France CISO Community here.
Give us a brief overview of the path that led to your current role.
I started in R&D as originally, I wanted to do a PhD and teach at university. I quickly realised that I liked to get my hands dirty and that was not the right path for me, so I pivoted and moved into penetration testing when this was barely a thing. Then, I added some consulting and compliance experience, particularly in the payment card industry, before becoming customer-facing and managing a small team.
After a few years in consulting, I realised that my clients struggled to evolve partly because they were missing the right people and expertise, so I decided to move on the other side. I quickly evolved through different roles, each time taking on more responsibilities driven by the idea that if I wanted to make the difference, I needed to be in charge.
But ultimately, my curiosity and eagerness to learn and try new things were my engine through those changes pushing myself out of my comfort zone.
What is one of your guiding leadership principles?
I will share three! Transparency, trust and accountability! These three ingredients are key to building strong and performant teams, but they are not easy to harvest. I recommend reading the excellent book "The Five Dysfunctions of a TEAM" by Patrick Lencioni to learn more.
What is the greatest challenge CISOs face today, and how are you addressing it?
"Shadow" AI/IT will continue to grow, and the world where technology was managed by ITD departments only will be gone. Nowadays, every consumer of technology can build applications quickly without expertise, and sometimes it comes with higher risks. The paradigm has shifted, and CISOs must adapt and extend their influence on everyone in the organisation, balancing control friction and user need and experience constantly.
Empathy is a great competency to understand why people behave the way they do, and so I put myself in someone else's shoes all the time to understand the context, what is at stake and decide.
What is the key to success for someone just starting out as a CISO?
Assuming most first-time CISOs climbed the ladder and came from a cybersecurity background, you most likely haven’t interacted as much as what you would need with the business. Make your way to business leaders and sit with them to understand their priorities, challenges, and gauge their cyber culture. Quickly identify your allies in the leadership team to sponsor your initiatives, and make sure to speak about business outcomes rather than cyber jargon.
How do you measure success as a leader?
The answer is simple: the day you are not needed anymore. Besides that provocative statement, I really think that once the culture of the organisation, top to bottom, leads to balanced decisions between business value and risk. This is utopia, so pragmatically I would measure maturity improvement, operational excellence, and the ability to deliver on ambitious goals.
What is the value of being a member of Gartner C-level Communities?
This is a great opportunity to meet with other senior leaders, sharing the same challenges and confronting our different perspectives and solutions. I like the saying "two heads are better than one" and the community allows access to other leaders' brains. This is a unique opportunity to meet so many leaders with direct interactions around key themes of the moment.
Governing Body members share their insights and leadership perspectives to shape the agendas and topics that address the top priorities impacting business leaders today.
By CISOs, For CISOs®
Find your local community and explore the benefits of becoming a member.